Preventative Security

Preventative Security Solutions — Engineer Out Risk Before It Becomes an Incident

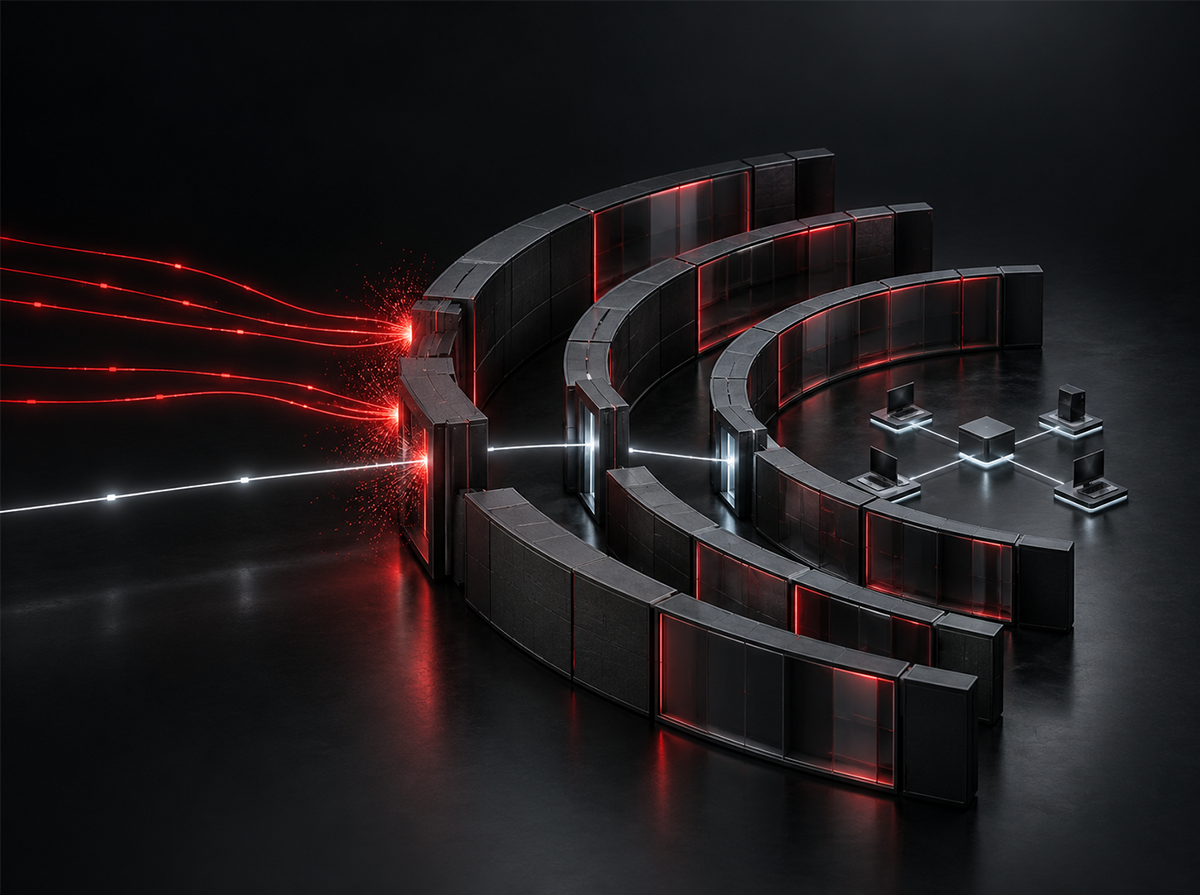
Design, build and harden the preventative controls that stop threats early: email and web security, endpoint and identity protection, network segmentation, data protection and secure configuration.

Preventative security • Security engineering • Defense in depth • Security hardening • Network segmentation • Email security • Endpoint protection • DLP • Security architecture UAE • Proactive cyber security
About
Preventative Security

How HexaPrime help you with Preventative Security!

Our Preventative Security Solutions service designs, deploys and hardens the technical controls that prevent attacks from succeeding. We start from your architecture, threat profile and existing investments, define a target-state control set mapped to recognised frameworks, and then engineer and integrate the controls so they work together as a defence-in-depth architecture rather than a collection of point tools. Engagements can cover greenfield design, tool deployment and tuning, remediation of assessment findings, or uplift of existing controls that are underperforming.

Key
Features
  • Defense-in-depth architecture
  • Email & web security engineering
  • Endpoint & server hardening
  • Identity & access hardening
  • Network segmentation
  • Data protection & DLP
  • Secure configuration & benchmarks
  • Control integration & automation
  • Regulatory alignment
Let’s Connect
Please send your work inquiry here...
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Workflow
Defence-in-Depth Control Architecture
<div class="sd" style="--n:6"> <div class="sd_dd"> <div class="sd_col"><span></span><div class="sd_side"><img class="sd_ico" src="https://cdn.prod.website-files.com/6a8df6c4166ed6e5454a4f94/6aa195fd499d76078cf49077_hxp-dd4-side-soc.png" alt="" loading="lazy"><h3 class="sd_t">External Threats</h3><p class="sd_d">Attacker Malware Exploits</p></div><span class="sd_drop"></span></div> <div class="sd_pyr"> <div class="sd_lyr" data-fl="1"><div class="sd_lh"><img class="sd_ico" src="https://cdn.prod.website-files.com/6a8df6c4166ed6e5454a4f94/6aa195fa5ac8beb7081bc2c4_hxp-dd4-01-perimeter.png" alt="" loading="lazy"><span class="sd_num">01</span><h3 class="sd_t">Perimeter &amp; Edge</h3><p class="sd_d">Email Security &bull; Web/DNS &bull; WAF</p></div> <div class="sd_lyr" data-fl="2"><div class="sd_lh"><svg class="sd_ico is-fig" viewBox="0 0 54 62"><path d="M25.8992 0.12506C26.3517 -0.041708 26.8634 -0.0416653 27.3185 0.12506L51.8547 9.08359C52.6682 9.38228 53.2124 10.1597 53.2125 11.0235V27.6128C53.2125 41.4763 45.0101 54.0589 32.3181 59.6668L27.4424 61.8222C27.1785 61.9406 26.8985 62 26.6077 62C26.3168 62 26.034 61.9406 25.77 61.8222L20.8943 59.6668C8.20233 54.0593 0 41.4763 0 27.6128V11.0235C2.94729e-05 10.1597 0.547005 9.37959 1.35777 9.08359L25.8992 0.12506ZM26.6081 1.37604C26.5274 1.37604 26.4466 1.39253 26.3712 1.41943L1.83499 10.3775C1.56564 10.4744 1.38256 10.7356 1.38256 11.0235V27.6128C1.38259 40.9328 9.26081 53.02 21.455 58.4072L26.3302 60.5631C26.5079 60.6411 26.7129 60.6411 26.888 60.5631L31.7632 58.4072C43.9567 53.0203 51.8361 40.9328 51.8361 27.6128L51.8337 11.0206C51.8337 10.7354 51.6506 10.4742 51.3813 10.3746L26.8451 1.41943C26.7697 1.38983 26.6889 1.37605 26.6081 1.37604Z"/><path class="r" d="M36.3463 22.8805C36.9943 22.2785 38.0093 22.3255 38.6115 22.9734C39.2129 23.6212 39.1674 24.6349 38.5202 25.237L24.4745 38.1698C24.1669 38.4512 23.7795 38.5964 23.3868 38.5964C22.9746 38.5962 22.569 38.4381 22.255 38.1241L15.606 31.4751C14.9777 30.8533 14.9777 29.8318 15.606 29.21C16.2277 28.5822 17.2478 28.5886 17.8695 29.21L23.4324 34.7729L36.3463 22.8805Z"/></svg><span class="sd_num">02</span><h3 class="sd_t">Network</h3><p class="sd_d">Segmentation &bull; Secure Zones &bull; NAC</p></div> <div class="sd_lyr" data-fl="3"><div class="sd_lh"><img class="sd_ico" src="https://cdn.prod.website-files.com/6a8df6c4166ed6e5454a4f94/6aa195faa884e0ac90461b00_hxp-dd4-03-identity.png" alt="" loading="lazy"><span class="sd_num">03</span><h3 class="sd_t">Identity</h3><p class="sd_d">MFA &bull; Conditional Access &bull; PAM</p></div> <div class="sd_lyr" data-fl="4"><div class="sd_lh"><img class="sd_ico" src="https://cdn.prod.website-files.com/6a8df6c4166ed6e5454a4f94/6aa195fac543de121ed6e3d8_hxp-dd4-04-endpoint.png" alt="" loading="lazy"><span class="sd_num">04</span><h3 class="sd_t">Endpoint</h3><p class="sd_d">EDR &bull; Hardened Baselines &bull; App Control</p></div> <div class="sd_lyr" data-fl="5"><div class="sd_lh"><img class="sd_ico" src="https://cdn.prod.website-files.com/6a8df6c4166ed6e5454a4f94/6aa195fa7fb1afc314ecd268_hxp-dd4-05-data.png" alt="" loading="lazy"><span class="sd_num">05</span><h3 class="sd_t">Data</h3><p class="sd_d">Classification &bull; Encryption &bull; DLP</p></div> <div class="sd_lyr" data-fl="6"><div class="sd_lh"><img class="sd_ico" src="https://cdn.prod.website-files.com/6a8df6c4166ed6e5454a4f94/6aa195fab5ea5844170bc0d4_hxp-dd4-06-governance.png" alt="" loading="lazy"><span class="sd_num">06</span><h3 class="sd_t">Governance</h3><p class="sd_d">Policy &bull; Secure Standards &bull; Monitoring</p></div> <div class="sd_core"><div class="sd_lh"><img class="sd_ico" src="https://cdn.prod.website-files.com/6a8df6c4166ed6e5454a4f94/6aa195fdc543de121ed6e454_hxp-dd4-core-assets.png" alt="" loading="lazy"><h3 class="sd_t">Protected Assets</h3></div><p class="sd_d">Applications &bull; Systems &bull; Critical Data</p></div> </div> </div> </div> </div> </div> </div> </div> <div class="sd_col"><span></span><div class="sd_side"><img class="sd_ico" src="https://cdn.prod.website-files.com/6a8df6c4166ed6e5454a4f94/6aa195fd7fb1afc314ecd49a_hxp-dd4-side-threats.png" alt="" loading="lazy"><h3 class="sd_t">SOC Monitoring &amp; SOAR</h3><p class="sd_d">Monitor Investigate Respond. Continuous visibility and automated response.</p></div><span class="sd_drop"></span></div> </div> <div class="sd_cyc"><span class="sd_pill">Continuous Improvement Cycle</span></div> </div>
Service Deliverables
Everything the service delivers. Built around measurable outcomes.
01
Current-State Control Review
  • Assessment of existing preventative controls, coverage and gaps against your threat profile and target frameworks.
02
Target-State Control Architecture
  • A defense-in-depth control architecture and design mapped to recognised frameworks and your risk priorities.
03
Implementation & Hardening Plan
  • A prioritised roadmap for deploying, tuning and hardening controls, sequenced by risk and dependency.
04
Deployed & Tuned Controls
  • Configured, integrated and validated preventative controls across the agreed scope.
05
Configuration & Hardening Standards
  • Documented secure baselines and configuration standards for ongoing enforcement.
06
Validation & Test Results
  • Evidence that deployed controls function as intended, including control testing and validation outcomes.
07
Operational Handover & Runbooks
  • Documentation, runbooks and knowledge transfer to enable your team to operate and maintain the controls.

See what Preventative Security Solutions delivers and how it fits your environment.

Talk to a Preventative Security Expert
FAQs
Frequently Asked Questions
How is this different from a security assessment?

An assessment tells you where you are exposed; this service engineers and deploys the controls that close those exposures. The two are complementary and are often delivered in sequence, with assessment findings feeding directly into a preventative controls roadmap.

Do we need to replace our existing security tools?

Usually not. We are vendor-agnostic and prioritise getting full value from tools you already own, deploying and tuning them properly before recommending any new investment, and only proposing new controls where a genuine capability gap exists.

Can you work from findings we already have?

Yes. Existing penetration test, vulnerability assessment or audit findings are an ideal starting point. We translate them into a prioritised, engineered remediation and hardening plan rather than a flat list of issues.

Will hardening disrupt our operations?

Changes are planned, tested and rolled out through agreed change control, typically in phases with pilot groups, so security uplift is achieved without unnecessary operational disruption.

Which frameworks do you align to?

Depending on your requirements, control design can align with CIS Controls and Benchmarks, NIST CSF, ISO/IEC 27001 and relevant UAE regulatory requirements.

Do you support ongoing operation of the controls?

Yes. We provide handover and runbooks for your team, and can offer ongoing managed operation and tuning of the deployed controls where required.

Ready to Secure Your Business?

Protect your organization with enterprise-grade cybersecurity, cloud, and managed IT solutions tailored to your business needs.